The Core Challenges of Securing Modern Software

Most CVEs Are Inherited
Base images and open source dependencies introduce risk before development begins.

Remediation Volume Outpaces Teams
Security teams cannot manually investigate and fix every scanner finding at release speed.

Runtime Risk Stays Hidden
Static scans do not show which components actually execute in production.
How RapidFort Secures the Software Supply Chain
RapidFort combines runtime visibility, secure image foundations, vulnerability analysis, automated hardening, and compliance validation into a single platform.
RapidFort Analyzer
Most scanners generate too much noise and too little context, making remediation slow and difficult to prioritize.
RapidFort Analyzer delivers validated vulnerability intelligence across images, registries, CI pipelines, and clusters so teams can reduce noise, focus on actionable risk, and accelerate remediation.

Curated Near-Zero CVE Images
Most applications inherit vulnerabilities from base images before development even begins.
RapidFort Curated Images provide hardened, production-grade base images with Near-Zero CVEs so teams can begin from a cleaner foundation and reduce inherited risk from the start.
RapidFort Profiler
Most teams cannot see which components actually execute in production, so theoretical risk gets treated the same as real exposure.
RapidFort Profiler reveals runtime behavior and generates RBOM® visibility so teams can focus on exploitable risk, identify active components, and make faster security decisions.
RapidFort Optimizer
Unused packages, binaries, and libraries silently expand software attack surface and increase exploitable risk.
RapidFort Optimizer removes unused components using runtime-validated intelligence, delivers hardened runtime images, and supports configurable hardening presets so teams can balance security depth with operational requirements.
RapidFort CART
Compliance evidence is often manual, point-in-time, and difficult to keep current across changing environments.
RapidFort CART continuously validates security baselines, generates audit-ready reports and remediation outputs, and helps teams maintain a more consistent compliance posture over time.
What Changes When Teams Deploy RapidFort

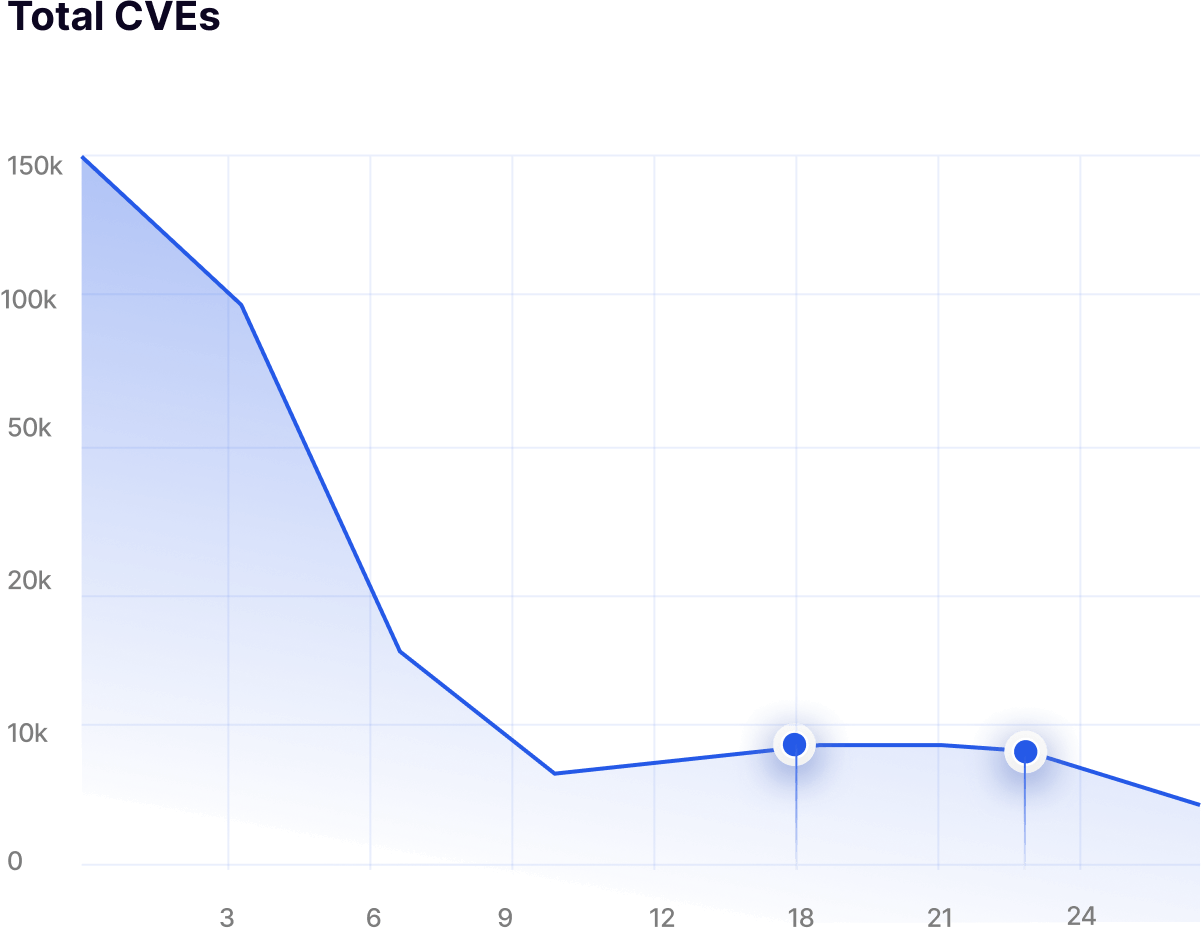
Up to 99.9% exploitable CVE reduction
Achieved by removing unused binaries, libraries, and OS components validated by RBOM® execution data.

90% Attack Surface Reduction
Driven by safely eliminating dormant binaries, packages, and libraries across container images.

Faster Incident Scoping
RBOM® visibility shows exactly which components are active in production environments.

Less Operational Friction
Continuous runtime profiling with less than 1% overhead and no application changes required.

Eliminate Attack Vectors at the Source
Continuously eliminate up to 99.9% of CVEs without code changes