Uncover the cost of remediation

RapidFort Business Value Calculator

Quantify Your Container Security ROI in Real-Time

Your Environment

Number of engineers in your development organization
Active containers requiring security patching
Fully loaded cost including benefits (USD)
Estimated annual platform investment
Requires zero-CVE compliance state

Key Assumptions

  • 10-15% of dev engineers or equivalent hours is spent on patching
  • 1 FTE needed per 10 containers for dedicated patching
  • 75% reduction in manual effort with RapidFort
  • FedRAMP timeline: 8 months → 2.5 months
  • Industry average: 102 days to deploy patches

Annual Cost Breakdown

Current Patching Costs (Dev + Dedicated) $0
FedRAMP Compliance (if applicable) $0
Total Current Annual Costs $0
With RapidFort (75% reduction) $0
RapidFort Platform Cost $0
Total With RapidFort $0
Net Annual Savings $0

Your ROI Analysis

Break-Even Timeline

Months to recover investment
0

Annual Savings

$0
Net benefit after RapidFort investment

ROI Percentage

0%
Return on investment

Break-Even Timeline Visualization

Month 1 Break-Even Month 12

Eliminate Attack Vectors at the Source

Continuous Threat Elimination from intake to runtime. Reduce up to 99.9% of vulnerabilities and 90% of your software attack surface, without code changes.

Real-time risk monitoring for immediate remediation

Reduction in Attack Surface and Image size reduction

Runtime Protection composes a baseline of container activity and instantly alerts your team when unusual behaviors are detected.

The result? Dev and security teams are armed with the insights they need to mitigate quickly and make impactful decisions. Drop runtime into your Kubernetes environment and say goodbye to CVE lifecycle management.

  • Cut dev drudgery and ship code when you need to
  • Make the most elegant, bloat-less code possible by knowing exactly what is (and isn’t) being used in the execution path
  • Get fully optimized from CI to CD – inform your buildtime process with runtime results
  • Free your dev team from alert fatigue and refocus them on meaningful work

Don’t accept risk – remove vulnerabilities automatically

Accurate and details report on unused components and Libraries for improving code and attack surfaces

Fully automate your remediation strategy – combine runtime monitoring with automated container hardening, all in one place. RapidFort’s comprehensive Software Attack Surface Management (SASM) platform enables DevSecOps teams to harden their software infrastructure – instantly. 

  • Automatically reduce your vulnerabilities and attack surface by 60-90%
  • Evolve your cybersecurity process and eliminate time spent on security reviews, triaging, patch management, mitigation, dependency management, etc.
  • Remove the busy work and refocus DevSecOps pros to meaningful security projects

Easy integration and immediate augmentation for your tech stack

Near-zero CVE Curated RF Images

What if you could take your current list of vulnerabilities and zoom in on the ones that lie within your execution path – and delete the rest? Shrink your workload in a matter of seconds and improve your current reporting with our execution path filter.

  • Get deeper, actionable visibility into your current reports
  • Quit burning expensive hours and effort on alert triage and get a full night's rest

Just a hot swap away

Augmented tech Stack

Runtime Protection is just a hot swap away. Simply deploy the helm chart in your Kubernetes cluster and RapidFort will automatically scan and profile pods, building a baseline of container activity.

  • No downtime for runtime clarity
  • Zero coding experience required 

Less than 1% compute overhead

Detailed Advisory

Have a massive, complex workload? RapidFort’s Runtime Protection will never require over 1% compute overhead to detect threats in real-time. No need to sacrifice your application size for modern cybersecurity monitoring. 

  • Predictable, low overhead
  • Save on space, save on costs
  • Receive immediate results regardless of your infrastructure size

Trusted by Your Peers.

Testimonial for RapidFort Platform
Testimonial from Chief Technology Officer for RapidFort Platform
Testimonial for RapidFort Platform
Testimonial from Chief Technology Officer for RapidFort Platform
Testimonial for RapidFort Platform

Why RapidFort

Understand how RapidFort stacks up to alternative solutions. Learn how Runtime Protection offers the most complete way for teams to secure their applications at runtime.

RapidFort
SCA scanner
EBPF Scanner
CWPP
Detect and prioritize vulnerabilities within the execution path
Tick icon
x-icon
Tick icon
x-icon
Monitor software usage at runtime
Tick icon
x-icon
Tick icon
x-icon
Automatically remediate and harden
Tick icon
x-icon
x-icon
x-icon
Compute overhead (worst case)
Less than 1%
N/A
10-20%
20-30%
Scan pipeline to runtime
Tick icon
x-icon
x-icon
x-icon

5 Reasons Why Leading Enterprises Choose RapidFort

choice-icon

DISA / DoD
Approved OS-Based Images

Includes integrated OpenSCAP STIG/CIS scanner

choice-icon

Complete End-to-End Platform

Near-Zero CVE images, Scanning, Profiling, Hardening, Benchmarking

choice-icon

Open Source not Single Source

Based on trusted LTS Linux distributions—Ubuntu, RHEL, Debian, Alpine — no vendor lock-in to proprietary OS

choice-icon

Patched vs Daily Build

RapidFort Near-Zero CVE images are patched with minimal code changes to ensure high reliability

choice-icon

Full Stack Optimization Effectiveness

Allows end customers to secure full-stack software (1st- and 3rd-party)

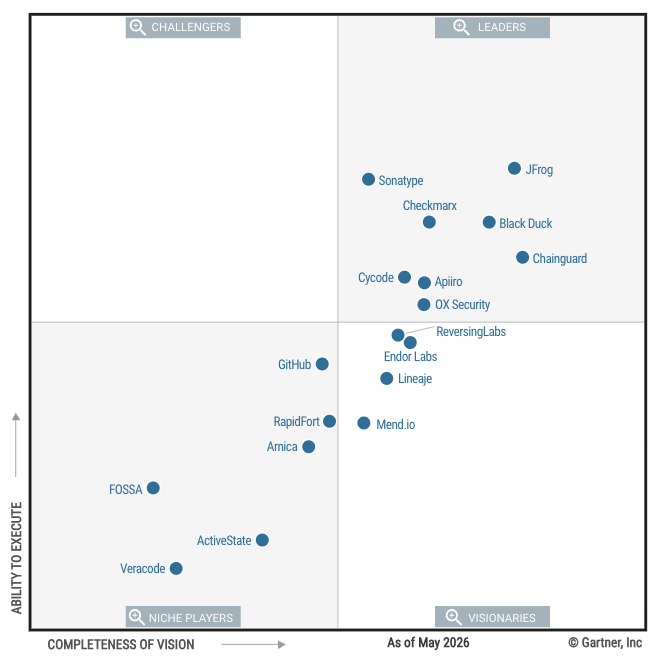
Ability to Execute

2026 Gartner® Magic Quadrant™

for Software Supply Chain Security

Get the Report