Continuous Security for Modern Software Teams

software banner image

Why Proving Product Security Is Hard

Workload management icon

Inherited Vulnerabilities

Container base images and open-source dependencies introduce vulnerabilities before development even begins.

Workload management icon

Security Evidence Gaps

Customers increasingly require proof of security posture during vendor risk reviews and procurement processes.

Workload management icon

Manual Remediation Cycles

Security teams spend significant time triaging vulnerability reports that often lack runtime context.

How RapidFort Reduces Software Supply Chain Risk

Prioritize True Risk with Analyzer and Profiler Intelligence

Blue hexagonal secure shield icon with a closed dot in top left and a ringed dot in bottom right inside the shape.
Identify exploitable vulnerabilities using deep binary analysis and runtime context
Blue hexagonal secure shield icon with a closed dot in top left and a ringed dot in bottom right inside the shape.
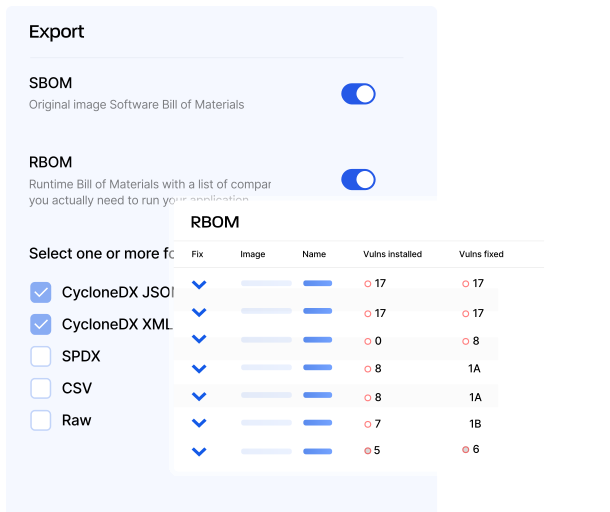
Generate SBOMs and Runtime Bills of Materials (RBOM®) for precise risk visibility
Blue hexagonal secure shield icon with a closed dot in top left and a ringed dot in bottom right inside the shape.
Reduce scanner noise by validating CVE applicability
Industry graphic
Industry graphic

Start Secure with Curated Near-Zero CVE Foundations

Blue hexagonal secure shield icon with a closed dot in top left and a ringed dot in bottom right inside the shape.
Deploy CIS and DISA STIG-aligned Curated Near-Zero CVE Images
Blue hexagonal secure shield icon with a closed dot in top left and a ringed dot in bottom right inside the shape.
Eliminate inherited vulnerabilities before development begins
Blue hexagonal secure shield icon with a closed dot in top left and a ringed dot in bottom right inside the shape.
Standardize hardened container foundations across engineering teams

Continuously Reduce Exposure with Optimizer and CART
Blue hexagonal secure shield icon with a closed dot in top left and a ringed dot in bottom right inside the shape.
Remove unused components to achieve up to 99.9% CVE reduction and up to 90% attack surface reduction
Blue hexagonal secure shield icon with a closed dot in top left and a ringed dot in bottom right inside the shape.
Enforce CIS and STIG baselines consistently across environments
Blue hexagonal secure shield icon with a closed dot in top left and a ringed dot in bottom right inside the shape.
Maintain a near-zero CVE posture with audit-ready evidence
Industry graphic

Outcomes Software Companies Can Rely On

Industry development icon

Up to 99.9% CVE reduction

Achieved through hardened base images and automated attack surface reduction.

Industry development icon

Up to 90% attack surface reduction

Delivered by removing unused binaries and dormant runtime components.
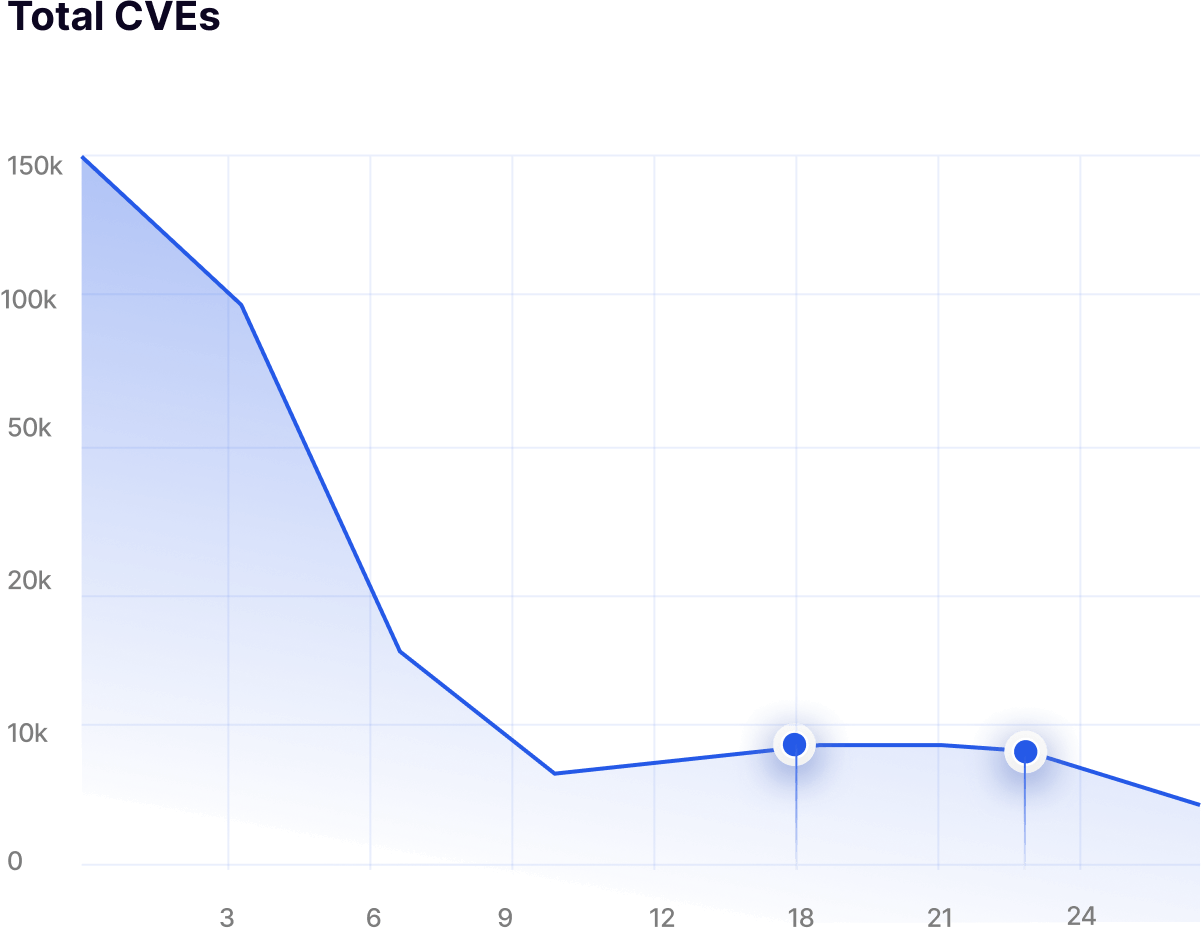
Area chart showing Total CVEs with values starting at about 150,000 at day 1, sharply decreasing to below 20,000 by day 6, then gradually fluctuating around 5,000 to 10,000 through days 12 to 24, with highlighted points at days 18 and 24.
Industry development icon

Faster audit preparation

SBOM, RBOM®, and configuration evidence remain continuously ready for review.

Industry development icon

About 60% less manual remediation effort

Automation replaces repetitive vulnerability triage, exception handling, and patch cycles.

Regulatory Evidence Built Into Every Release

Regulatory compliance icon

SOC 2 Type II Alignment

Continuous vulnerability visibility and hardened container foundations support SOC 2 security controls.

Regulatory compliance icon

ISO/IEC 27001 Alignment

Secure container foundations help maintain consistent infrastructure security controls.

Regulatory compliance icon

FedRAMP and CRA-Aligned Customers

Hardened container images support SaaS providers selling to regulated US and EU environments.

Regulatory compliance icon

Customer Security Reviews

Provide SBOMs, vulnerability visibility, and hardened foundations that simplify vendor security assessments.

Frequently Asked Questions

Answers to Your Most Common Questions

What is RapidFort?
arrowarrow
Does RapidFort cover the whole software lifecycle, or just one stage?
arrowarrow
What problem does RapidFort solve?
arrowarrow
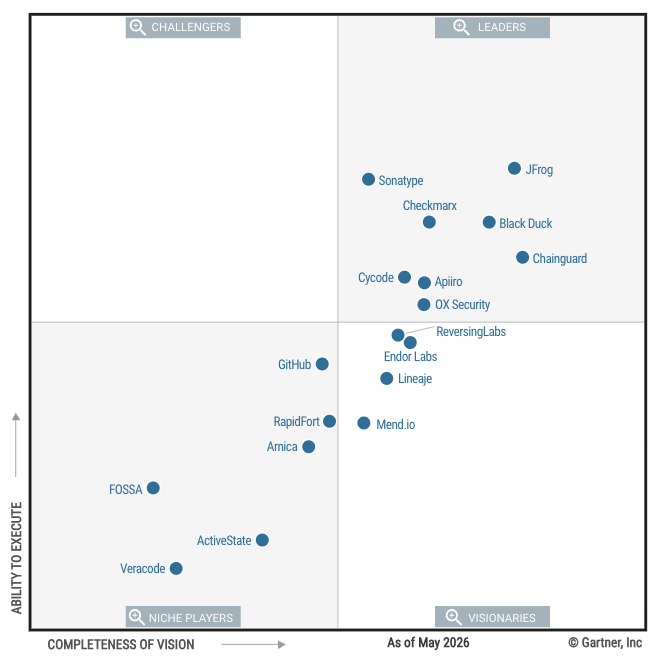
Ability to Execute

2026 Gartner® Magic Quadrant™

for Software Supply Chain Security

Get the Report