Why Financial Workloads Stay Exposed
Inherited Vulnerabilities
Base images and third-party software introduce risk before development even begins.
Remediation Noise
Scanner overload makes it harder to focus on the vulnerabilities that actually matter.
Audit Gaps
Point-in-time reviews struggle to keep up with modern release cycles and changing environments.
How RapidFort Reduces Financial Software Risk
Prioritize True Risk with Analyzer and Profiler Intelligence
Start Secure with Curated Near-Zero CVE Foundations
Continuously Reduce Exposure with Optimizer and CART
Outcomes Financial Institutions Can Rely On
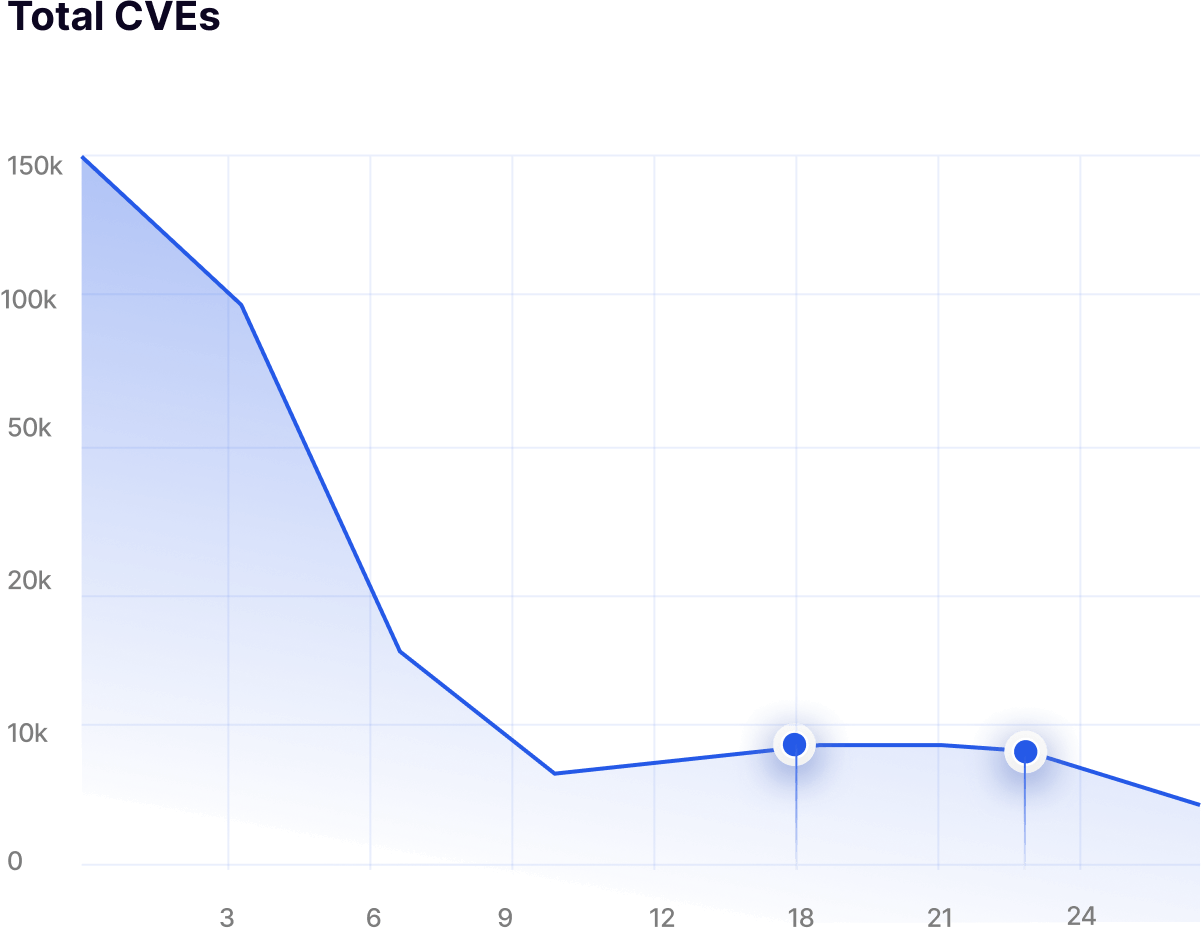
Up to 99.9% CVE elimination
Achieved through hardened base images and automated attack surface reduction.
Up to 90% attack surface reduction
Delivered by removing unused binaries and dormant runtime components.
Faster audit preparation
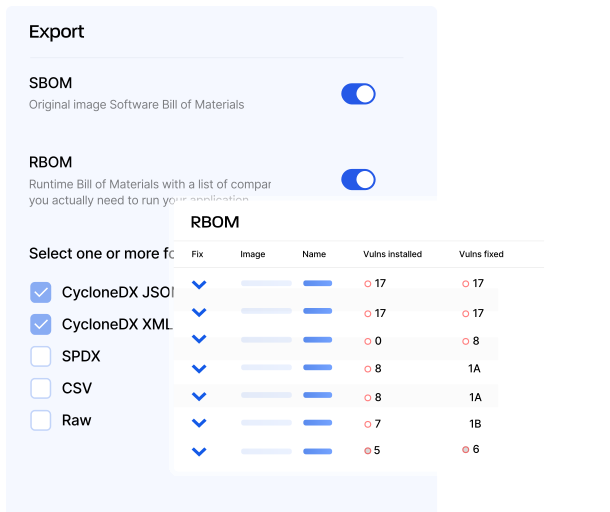
SBOM, RBOM®, and configuration evidence remain continuously ready for review.
About 60% less manual remediation effort
Automation replaces repetitive vulnerability triage, exception handling, and patch cycles.
Regulatory Evidence Built Into Every Release
PCI DSS support
Validated vulnerability intelligence and runtime visibility strengthen control verification.
SOX-aligned change assurance
Runtime and configuration visibility support stronger control monitoring.
Hardened regulatory baselines
CIS and STIG-aligned foundations improve consistency across regulated workloads.
Continuous audit evidence
Structured artifacts simplify internal reviews and external assessments.
Frequently Asked Questions
Answers to Your Most Common Questions
RapidFort is an end-to-end software supply chain security platform for containerized applications that covers Intake, Build, and Runtime. It eliminates up to 99.9% of CVEs (Common Vulnerabilities and Exposures) and reduces the software attack surface by up to 90%, without code changes, operating system changes, or pipeline modifications.
It does this with RapidFort Curated Near-Zero CVE Images, which RapidFort engineers manually patch and rebuild; RapidFort Curated Libraries, a catalog of malware-scanned open source libraries; runtime-aware hardening; and continuous production monitoring. RapidFort was founded in 2020.
RapidFort covers the whole lifecycle: Intake, Build, and Runtime in one end-to-end platform, with no gaps, no handoffs, and no blind spots.
Intake: risk is eliminated before entry, with drop-in curated near-zero CVE images and malware-scanned open source libraries. Build: components are hardened and the attack surface is reduced, guided by RBOM® (Runtime Bill of Materials) showing what your application actually runs. Runtime: environments are continuously monitored and protected, with drift detection and audit-ready compliance evidence.
Instead of separate tools for scanning, SBOMs (software bills of materials), and runtime, one platform covers every stage.
RapidFort eliminates vulnerabilities that organizations inherit from software they run but do not control. More vulnerabilities are introduced than engineers can reasonably fix, and security teams are overwhelmed by alerts and false positives.
Attackers do not wait. Under CISA (Cybersecurity and Infrastructure Security Agency) Binding Operational Directive 26-04, vulnerabilities in the CISA Known Exploited Vulnerabilities (KEV) catalog carry federal fix deadlines of 3 or 14 days. RapidFort eliminates attack vectors at the source, before they reach production.