Tens of thousands of curated images, hardened and rebuilt every 24 hours. Every patchable CVE eliminated, with CISA KEV severity fixed within 24 hours, critical and high in 7 days, moderate in 21 days, and low in 28 days. Adoption is one line in your Dockerfile.
Capability
Rapidfort Curated Images
aikido Hardened Images
All patchable CVEs eliminated
Documented as critical and high severity, with application packages on best effort
CISA KEV in 24 hours, critical and high in 7 days, moderate in 21 days, and low in 28 days.
CISA KEV in 48 hours, critical and high in 7 days, medium and low in commercially reasonable SLA.
Tens of thousands of curated images
2,000+ images
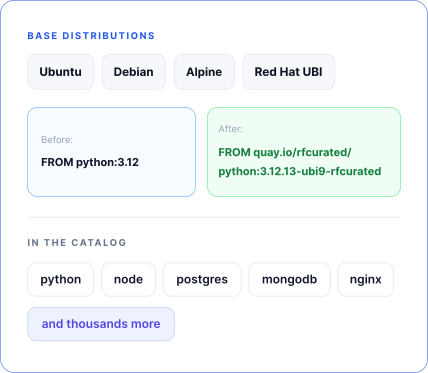
Genuine upstream Ubuntu, Debian, Alpine, and Red Hat UBI
Patches the base you already run, same family and major version
Hardened to CIS and DISA STIG, FIPS 140-3 builds, available in Iron Bank
FIPS images offered; no STIG or CIS variants published
Runtime profiling and optional removal of components that never execute
Network reachability analysis, not execution profiling
Non-FIPS versions of RapidFort base images and libraries are PQC-ready (Post quantum cryptography ready)
N/A
Software Supply Chain Security
Verified customer reviews
DISA validated hardened images
Trusted in production

"We eliminated our CVE backlog without touching a single Dockerfile. The runtime profiler paid for the platform in the first sprint."
"We eliminated our CVE backlog without touching a single Dockerfile. The runtime profiler paid for the platform in the first sprint."
"We eliminated our CVE backlog without touching a single Dockerfile. The runtime profiler paid for the platform in the first sprint."


RapidFort Curated Images are built on genuine upstream distributions, with the full patch version pinned in the tag. You point the image reference at a curated tag and rebuild.
Your Dockerfiles and application code
Your Linux distribution and major version
Your registry, CI pipeline, and scanner
Your pinned minor and older versions
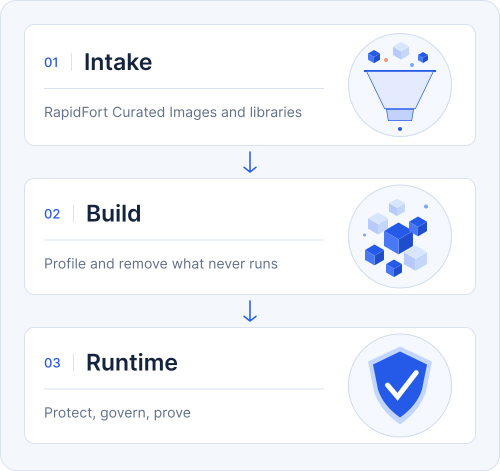
Your team layers software on top of that base image, and that layer is where the rest of your CVEs live. Runtime profiling records what actually executes, so everything that never runs can be optionally removed.
CVE elimination
attack surface reduction
Catalog images hardened to DISA STIG and CIS Benchmarks.
FIPS 140-3 builds for workloads with cryptographic requirements.
Available in Iron Bank and deployable on premises via Big Bang.
SBOM export in SPDX, CycloneDX, JSON, and CSV, with VEX support.
Every container CVE its own BOD 26-04 compliant live remediation clock
off the FedRAMP timeline
lower Secure SDLC and image hardening cost
Engineering Manager, Site Reliability Engineering, Beyond Identity
Search the catalog for the images, versions, and base distributions you run.
Point the build at the curated tag, then run your existing tests and scanner.
Daily rebuilds keep the base current. Add runtime profiling when you are ready.

Request access, swap one image, and compare the scan output against the base you run today.