
A drop-in, security-hardened container builder engineered for
compliant, verifiable builds in modern cloud-native environments.
Migration from Kaniko
Just swap the image reference
True Rootless Operation
No root, no daemon, no privileges
Native Attestation
SPDX 2.3, Sigstore Cosign signing
01
Kaniko is now sunset and no longer actively maintained. Organizations that depend on secure, daemonless container builds face a growing challenge: how to keep building images safely, reproducibly, and in compliance with modern security standards.
RapidFort Kimia, an open-source project developed by RapidFort in collaboration with SOSi, is engineered as the natural successor to Kaniko. It provides full backward compatibility while delivering meaningful advances in security, reproducibility, and enterprise readiness.
Kimia preserves everything that made Kaniko valuable: daemonless builds, Kubernetes-native workflows, and straightforward adoption. It pairs that foundation with an architecture built for today's security-conscious environments, including true rootless operation, user namespace isolation, minimal Linux capabilities, reproducible builds, and real-time SBOM and provenance generation. The result is a build pipeline that functions as a secure, verifiable, and fully auditable part of the software supply chain.
Kimia offers a straightforward migration path for existing Kaniko users, requiring only a one-line image update and minimal Kubernetes security context changes. Teams gain a hardened, compliant, and efficient container build process, designed for modern cloud-native infrastructure and actively maintained going
RapidFort Kimia is available on GitHub under an open-source license:
RapidFort Kimia is part of RapidFort's broader mission to eliminate software supply chain risk at the source. Where RapidFort Curated Images and RapidFort Curated Libraries secure what enters the pipeline, Kimia secures how that pipeline builds, extending elimination-first security into the build stage itself.
02
Kaniko changed Kubernetes-native image building by removing the need for a privileged Docker daemon. Its deprecation, however, has created a real operational and security gap. As threats increase and compliance mandates tighten, organizations cannot depend on an unmaintained builder, particularly one that still runs as root and lacks modern supply chain protections.
Runs as UID 0, increasing container escape risk.
Limits defense-in-depth for build workloads.
No native provenance or software bill of materials.
Constrained Dockerfile support, especially for chown and complex ownership rules.
Meets only the Kubernetes "Baseline" Pod Security Standard.
Security gaps persist with no ongoing fixes.
Modern DevSecOps teams need more than image assembly. They need secure, attested, and verifiable builds that reduce risk and meet compliance requirements without slowing developers down. RapidFort Kimia was engineered to meet that need directly.
Root (UID 0)
No user namespaces
No SBOM / provenance
Baseline PSS only
Unmaintained
Rootless (UID 1000)
User namespace isolation
SPDX 2.3 SBOM + provenance
Restricted PSS compliant
Actively maintained
03
RapidFort Kimia provides a one-to-one functional replacement for Kaniko while introducing a hardened execution model and a more advanced security architecture. Migration requires only minimal changes.
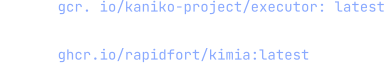
All major Kaniko arguments work exactly the same way in Kimia, with full compatibility across core flags, including --context, --dockerfile, --destination, --build-arg, --cache , --cache-dir, --insecure, and --skip-tls-verify, among others. Git context builds are compatible as well, and capabilities Kaniko lacked, such as reproducible output, are now native to the platform.
This argument-level compatibility allows organizations to migrate in minutes rather than weeks, with no disruption to existing CI/CD pipelines.
04
Kimia's design reflects contemporary security requirements and lessons learned from years of running Kaniko in production. Four pillars define its security architecture.
Kimia runs as UID 1000, never as root, reducing the blast radius of container escapes and enabling safe use in regulated and multi-tenant environments.
Unlike Kaniko, Kimia maps container UID 0 to host UID 1000, adding a mandatory security boundary that makes privilege escalation far more difficult.
Kimia requires only SETUID and SETGID. All other capabilities are dropped: no privileged mode, no SYS_ADMIN, no daemon.
Kimia is fully compliant with the strictest Kubernetes security profile, aligning secure builds with modern cluster hardening and government compliance frameworks.
05
As supply chain security becomes a priority across industries, reproducibility and attestation are no longer optional. Kimia includes these capabilities natively.
Kimia supports bit-for-bit deterministic output, ensuring that the same source and Dockerfile produce identical images every time. This is a foundational requirement for SLSA compliance and forensic verification.
Kimia generates a real-time SPDX 2.3 software bill of materials, providing a full inventory of packages and dependencies. This supports continuous vulnerability scanning and compliance reporting.
Kimia emits verifiable build metadata, including build time, environment, builder identity, and source context.
Native Sigstore Cosign support allows images to be cryptographically verified before deployment.
06
Kimia expands on Kaniko's instruction support with full chown and ownership operations, advanced multi-stage build handling, support for Docker-specific instructions such as HEALTHCHECK, SHELL, and STOPSIGNAL when using Docker output format, OCI and Docker-compatible build outputs, and multi-architecture build support, including --custom-platform=linux/arm64
Kimia runs seamlessly in Kubernetes clusters, Docker environments, local Cl runners, and any OCI-compliant registry, public or private. It also supports concurrent builds, isolated through user namespaces.
CPU overhead relative to Kaniko
RAM depending on build complexity
core flag compatibility with Kaniko
Kimia supports caching through --cache and --cache-dir , is compatible with overlay and VFS storage drivers, and is designed for parallel execution at scale. Documented resolutions exist for common operational issues such as namespace errors, permission conflicts, and cache directory restrictions. Kimia also supports Git-based contexts, distroless images, and deployment in regulated environments.
07
Kimia is the right choice when security, compliance, or complex build requirements matter.
Defense-in-depth security for production builds; compliance with Kubernetes "Restricted" Pod Security Standards; verification; attestation, SBOM, and image signing; complex Dockerfile compatibility; or deployment in regulated industries such as PCI DSS, HIPAA, SOC 2, and government or defense environments.
Defense-in-depth security for production builds; compliance with Kubernetes "Restricted" Pod Security Standards; verification; attestation, SBOM, and image signing; complex Dockerfile compatibility; or deployment in regulated industries such as PCI DSS, HIPAA, SOC 2, and government or defense environments.
For modern, security-focused environments, Kimia offers a hardened and fully verifiable path forward. The migration takes minutes and provides immediate, measurable security improvements with no disruption to existing CI/CD workflows.
08
Kimia preserves everything users value in Kaniko: daemonless builds, CI/CD simplicity, and Kubernetes-native workflows. It pairs that foundation with the security, compliance, and reproducibility that modern software supply chains demand.
As the actively maintained, fully compatible successor to Kaniko, Kimia enables organizations to modernize their container build pipeline, adopt secure and rootless builds isolated by user namespaces, generate verifiable and signed images, reduce exposure to supply chain attacks, and meet the strictest compliance standards.
With Kimia, secure container builds become the default rather than an afterthought, giving organizations a future-ready, drop-in replacement for Kaniko.

RapidFort is the leader in Software Supply Chain Security, enabling organizations to eliminate risk across their software stack at scale. Its platform combines curated near-zero CVE container images, runtime profiling, and attack surface management to remove up to 99.9% of vulnerabilities within hours and reduce the attack surface by up to 90%, without code changes. RapidFort was identified as a Gartner Cool Vendor in 2025 and a Nutanix .Next Partner of the Year in 2026.
© 2026 RapidFort, Inc.


